Analysis
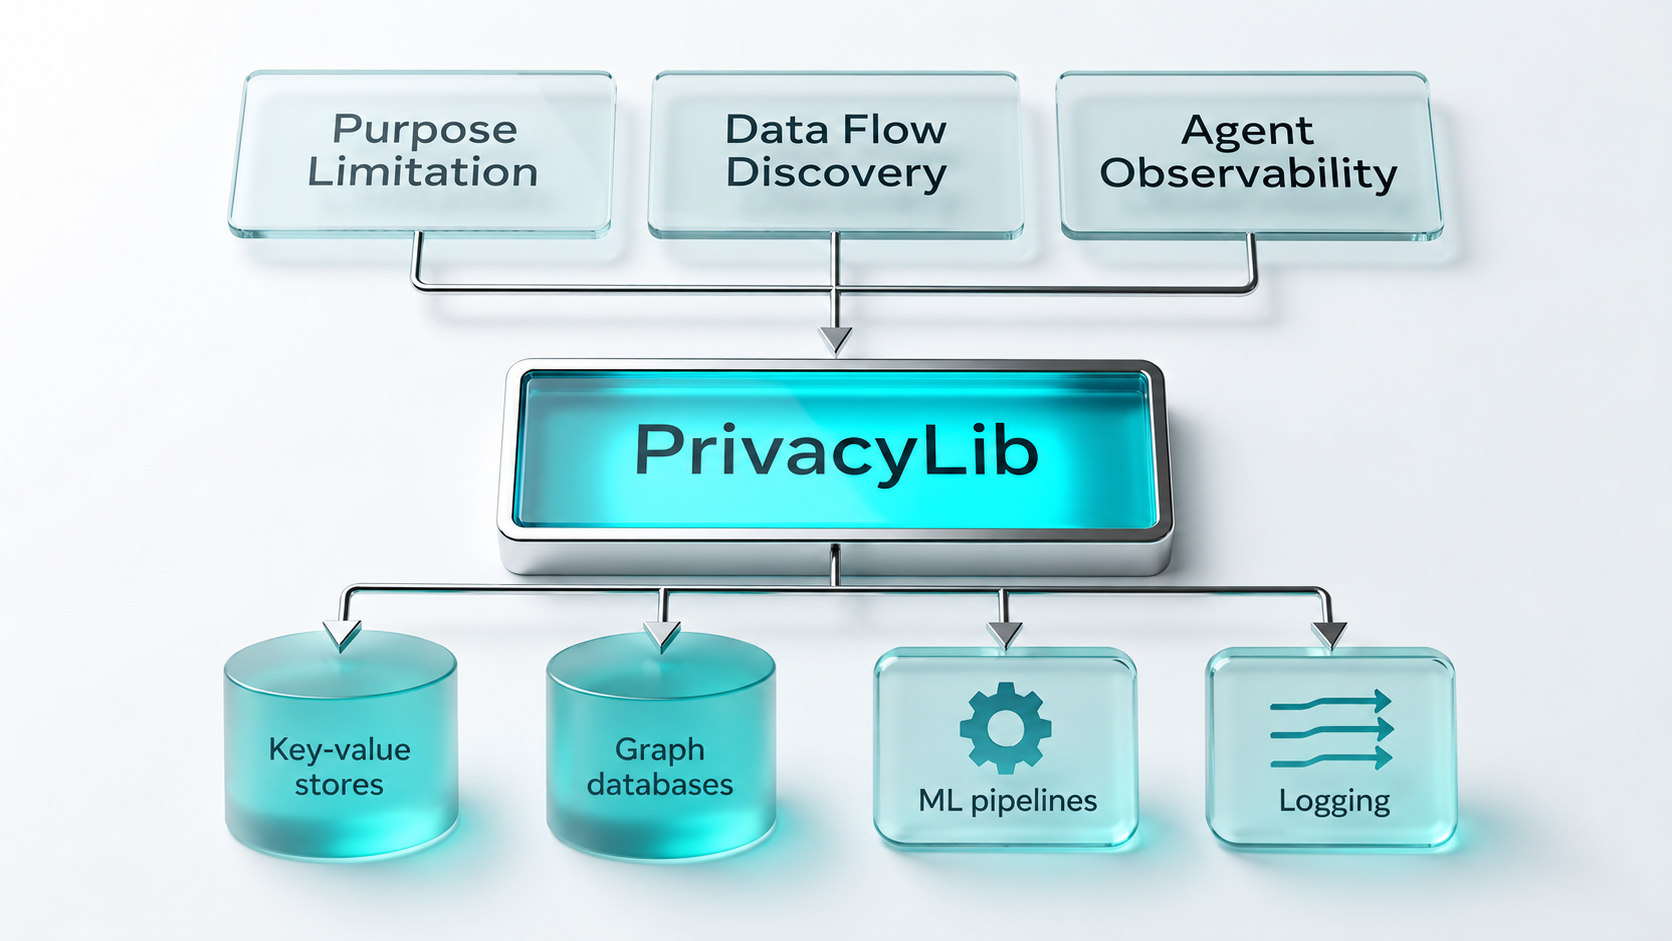
Meta’s October 27 engineering account describes PrivacyLib, a common library embedded in clients that access its data and processing systems. An integration can serve several privacy modules, reducing the need to rebuild controls separately for every new requirement. Meta says the library performs billions of checks each second across its infrastructure.
The distinction between observing and enforcing matters. Some modules record access; others can refuse it. For supported internal-agent paths, tool calls carry session context through services to the data boundary, where an enabled policy can block an operation. Meta explicitly says paths outside its managed clients and supported RPC boundaries need their own integration.
Our reading: this puts a useful test of agent control in a concrete place. A well-behaved assistant is not sufficient evidence that information stayed within its permitted use. The stronger question is whether the eventual read or write was checked, with the right destination and context, even when the agent chose an unexpected tool.
Coverage also has a release history. Meta describes simulations before annotation changes and staged module rollouts. A system inventory therefore needs to record which version is deployed, not merely whether a library was once integrated. The company’s design account supplies an architecture to examine; it does not independently establish complete protection across every data path.
Source: PrivacyLib: Privacy Controls at the Data Access Boundary · 2026-10-27
Why it matters
An access control only helps when the actual route to the data passes through it.