Analysis
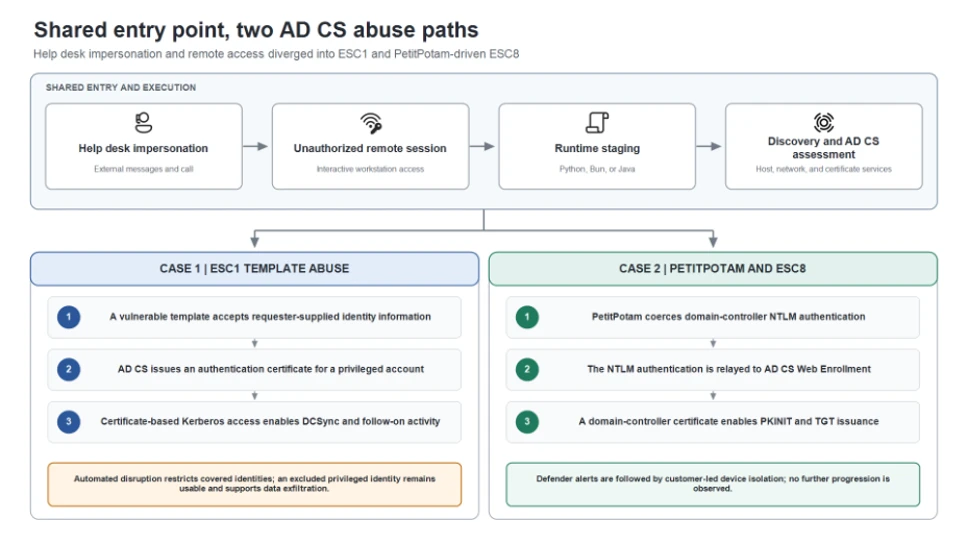
Microsoft Threat Intelligence described two human-operated intrusions on October 30 that began the same way: Teams messages and calls impersonating IT or help desk staff, which persuaded users to approve a remote session, mostly through Quick Assist. The attackers then staged portable Python, Bun or Java runtimes from user-writable folders and began assessing Active Directory Certificate Services.
The cases split at the certificate layer. In the first, a template that let the requester supply identity information yielded certificates for privileged accounts, followed by DCSync; one privileged account had been excluded from automated containment and was later used to copy data out with Rclone. In the second, the attacker coerced domain controller authentication with PetitPotam and relayed it to AD CS Web Enrollment to obtain a domain controller certificate. Defender alerts led that customer to isolate the workstation, and Microsoft observed no further progression.
Our reading: the social engineering was the door, but the certificate configuration decided how far the intruder could walk. Microsoft’s recommendations follow that shape: verify unsolicited support contact through known channels and restrict external Teams access, but also review templates, remove unneeded enrollment rights and Web Enrollment endpoints, require HTTPS with Extended Protection, and audit issuance. Revoking a certificate, Microsoft notes, does not invalidate Kerberos tickets already issued.
The first case adds an operational point. An exclusion from automated containment is an incident decision, and it needs compensating controls rather than quiet permanence. Microsoft does not attribute the activity to a named actor, and its hunting queries are starting points that need tuning. A useful review asks which templates accept requester-supplied names, where Web Enrollment is exposed, and which accounts are exempt from containment.
Source: From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths · 2026-10-30
Why it matters
Certificate templates, enrollment endpoints and containment exceptions determine whether a convincing support call becomes domain-wide compromise.